

Commission disclosure: This article includes one promotional link to a commercial product. The guidance below is educational and applies whether you use that product or any similar hosted AI agent.
If you are thinking about using a hosted AI agent, the main issue is not whether it sounds powerful. It is whether you understand what it can access, who can see your data, and what happens if something goes wrong. That matters for solo users, freelancers, founders, and small teams that may want convenience without handing over unnecessary control.
InstantlyClaw Premium is one example of a hosted option, but the safety questions in this guide apply to all similar tools. Before you upload files or connect accounts, use the checklist below to test the boundaries, not the marketing.
Direct Answer & Introduction
What you need to know first
A hosted AI agent can save setup time, but it can also increase your exposure if you do not understand permissions, storage, and approval flows. The core safety questions are straightforward: what data is stored, where it is stored, who can access it, whether actions require confirmation, and how you disconnect the system if needed. If a seller cannot answer those clearly, pause before sharing anything sensitive.
Who this guide is for
This guide is for non-technical readers who want practical ways to reduce risk before using a cloud-based AI assistant. The goal is not to remove every risk. It is to make a more informed choice and avoid handing over more access than the task requires.
Fundamentals
Hosted versus local in plain language
A hosted AI agent runs on someone else’s servers rather than on your own device. That can be helpful because it avoids local installation and ongoing maintenance, but it also means your data may pass through infrastructure you do not control. A local setup keeps more activity on your machine, but then your device security becomes part of the risk.
Access, permissions, and approvals
Access means what the agent is allowed to connect to, such as email, documents, messaging apps, or calendars. Permissions are the rules that limit what it can do. Approvals are the checkpoints that require you to confirm a sensitive action before it happens. In practice, “approval required” is one of the most useful safety features because it can stop accidental sending, deletion, posting, or billing.
Data handling terms worth understanding
Ask whether the service stores your prompts, uploaded files, outputs, logs, and account tokens. Ask how long each item is retained, whether it is used to improve the service, and whether you can delete it. If the answers are vague, treat that vagueness as a risk signal. Clear language is usually a better sign than broad claims about being “secure” or “private.”
Main Process / Strategies
Step 1: Map the data before you connect anything
Start by listing the kinds of information the agent would touch. Separate low-risk content, such as public marketing text, from higher-risk content, such as client contracts, customer records, invoices, internal strategy notes, and login-connected tools. A practical rule: do not assume “useful to the business” also means “safe to share with a new platform.”

Example: A freelancer might let a hosted agent draft social captions from a style guide, but keep it away from inbox access until they confirm how mailbox data is stored, logged, and protected.
Step 2: Ask about storage, retention, and deletion
Before any upload, ask where files and conversation history live, whether they are encrypted in transit and at rest, how long logs are kept, and whether deletion is permanent or delayed. Also ask what happens to backups. A service can say it “deletes” data and still keep backup copies for a period of time. That is not automatically bad, but it should be disclosed plainly.
Step 3: Test the approval model with a real scenario
Imagine the agent is preparing an outreach campaign. Without approval rules, it might draft, schedule, or send messages that you have not reviewed. With approval rules, it can prepare the work, but the final send action pauses until you confirm. That difference matters because many costly mistakes are not about the draft itself; they happen at the final action step.
Worked scenario: A small agency uses a hosted AI agent to prepare client follow-up emails. The agent can read a project brief and write drafts, but it cannot send anything without approval. If the draft contains the wrong recipient, the owner catches it before delivery. If the platform also records approval history, the team can audit what was sent and why.
Step 4: Check the boundary between the tool and your accounts
Ask whether the agent has full account access, limited API access, or session-based access that expires. If it can post, delete, send, or purchase on your behalf, confirm whether those actions are blocked by default or only protected by a prompt. Limitations should be clear enough that you can explain them to a colleague without guessing.
A useful question is: “If I disconnect this today, what access remains?” That tells you whether the platform is using temporary tokens, persistent tokens, or broad account permissions that are hard to revoke.
Step 5: Review human oversight and failure handling
Good hosted systems should make it easy to stop a workflow, review its output, and disconnect or revoke access. Ask what happens when the model is wrong, when a workflow loops, or when a tool call fails. You want to know whether the platform logs errors clearly enough for a non-engineer to understand, not just whether it can technically recover.
Example: If an agent is set to summarize leads from a spreadsheet, you should know whether a failed row simply gets skipped or whether the whole workflow retries and possibly duplicates work.
Step 6: Use a short pre-share checklist
Before you upload anything, ask these questions in plain English:
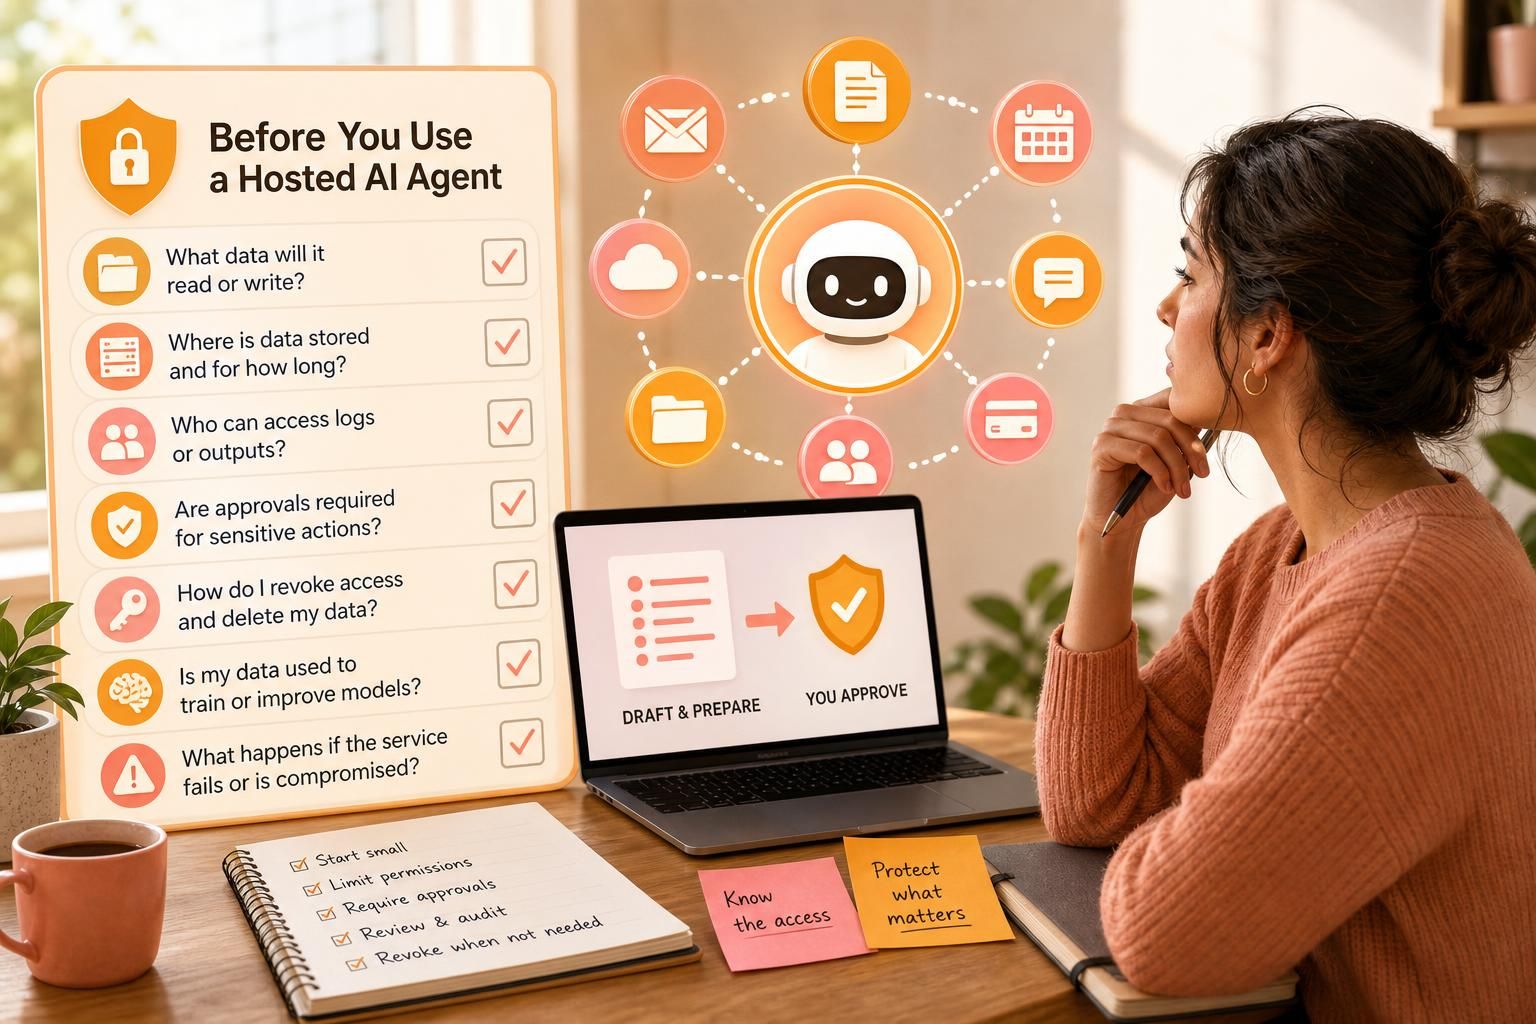
- What exactly will this tool read or write?
- Where is the data stored, and for how long?
- Who inside the company can access logs or outputs?
- Can I require approval before send, delete, publish, or purchase actions?
- How do I revoke access and delete my data?
- Is my data used to train models or improve the service?
- What happens if the service is compromised or the workflow fails?
If a seller can answer those clearly, you are in a much better position than if you rely on broad convenience claims.
FAQs, Mistakes & Expert Insights
Common mistakes to avoid
Mistake 1: Assuming hosted automatically means safer. Hosting removes some technical burden, but it does not remove the need to understand permissions and retention. A cloud service can still be risky if it has broad access to sensitive data.
Mistake 2: Treating “approval” as optional. Approval checkpoints are often the difference between a draft and an irreversible action. If a tool can send, delete, or post, confirmation matters.
Mistake 3: Sharing full access too early. Start with low-risk data and narrow permissions. Expand only after you understand the platform’s behavior and documentation.
Mistake 4: Confusing marketing language with control. Claims like “secure,” “protected,” or “private” are not enough on their own. You need concrete answers about storage, logging, and revocation.
Mistake 5: Ignoring what happens after disconnect. If you cannot quickly revoke access, the platform may be harder to manage than it first appears.
Nuanced insight: convenience and risk often rise together
The more a hosted AI agent can do for you, the more important its guardrails become. That does not mean powerful systems are unusable. It means the safest workflow is usually one where the agent drafts, organizes, and prepares work, while you approve sensitive steps. Convenience is valuable, but it should not hide the fact that access boundaries are a security feature, not a limitation to work around.
FAQ
What is the most important question to ask first?
Ask what the agent can read, write, send, delete, or purchase. That single question reveals the practical boundary of the tool and helps you judge whether the risk matches the task.
Is a hosted AI agent unsafe by default?
No. Hosted tools can be reasonable when permissions are limited, approvals are required for sensitive actions, and data handling is clearly documented. The issue is not hosting itself; it is unmanaged access.
Do approval steps really make a difference?
Yes. Approvals can stop irreversible actions from happening automatically. They are especially useful for email, publishing, file deletion, and account-connected tasks where a mistake can spread quickly.
What should I ask about data retention?
Ask whether prompts, files, outputs, and logs are stored, how long they are kept, whether they are used for training or service improvement, and how deletion works. If the answer is unclear, do not assume the data disappears right away.
What is a safe way to start?
Begin with low-risk content and a narrow use case, such as drafting non-sensitive copy or organizing public information. Test approval settings, revocation, and deletion before you connect anything confidential.
InstantlyClaw Premium can be a starting point for understanding how a hosted setup works, but the same questions apply to any vendor. For more context on fit and setup tradeoffs, see how to tell whether a hosted AI agent setup is worth paying for, what a hosted AI agent setup usually includes, and beginner workflows you can test with a hosted AI agent system.
What is the most important question to ask first?
Ask what the agent can read, write, send, delete, or purchase. That single question reveals the practical boundary of the tool and helps you judge whether the risk matches the task.
Is a hosted AI agent unsafe by default?
No. Hosted tools can be reasonable when permissions are limited, approvals are required for sensitive actions, and data handling is clearly documented. The issue is not hosting itself; it is unmanaged access.
Do approval steps really make a difference?
Yes. Approvals can stop irreversible actions from happening automatically. They are especially useful for email, publishing, file deletion, and account-connected tasks where a mistake can spread quickly.
What should I ask about data retention?
Ask whether prompts, files, outputs, and logs are stored, how long they are kept, whether they are used for training or service improvement, and how deletion works. If the answer is unclear, do not assume the data disappears right away.
What is a safe way to start?
Begin with low-risk content and a narrow use case, such as drafting non-sensitive copy or organizing public information. Test approval settings, revocation, and deletion before you connect anything confidential.
Summary & Next Steps
Your practical decision framework
If a hosted AI agent cannot clearly explain permissions, storage, retention, approvals, and revocation, do not treat it as ready for sensitive work. If it can explain those things in plain language, start with low-risk tasks and expand slowly. That approach protects your data while still letting you benefit from automation.
What to do next
Make a short checklist before you sign up: define the data you want the tool to touch, ask how it stores and deletes that data, confirm whether sensitive actions require approval, and verify how to disconnect the service. If you want a broader cost-and-fit framework after that, move next to the commercial overview and the setup/cost guides in the cluster.
For a deeper comparison of value, see the pillar article on InstantlyClaw Premium Review: Hosted OpenClaw Setup, Costs, Features, and Who It Fits. For adjacent practical guidance, review how to estimate the real cost of running an AI agent tool and what an AI agent setup usually includes.

[…] security-specific due diligence, the companion article on security and privacy questions to ask before using a hosted AI agent goes deeper into risk […]